 War of the Ecosystems
Request Strategy Session

The most dangerous artificial intelligence workflow failure may not look like a dramatic model hallucination.
It may look like a normal comment, a routine ticket, a helpful instruction, a workflow field, a pull-request note, or a support message that quietly becomes part of an agent's operating context.
That is why agentic workflow security has to move upstream.
Executives often talk about artificial intelligence agents as if the risk begins when the model decides something. That is too late. In real operating workflows, risk starts earlier, at the point where outside information enters the system, gets transformed into context, and reaches an agent that can use tools.
The research paper Comment and Control: Hijacking Agentic Workflows via Context-Grounded Evolution is a useful warning sign. The authors study agentic workflows in automation platforms, including GitHub Actions and n8n-style templates. Their core concern is direct enough: untrusted inputs, such as GitHub issue comments, can be crafted so that they enter the large language model context and influence an agent that has runtime capabilities. The reported consequences include credential leakage and arbitrary command execution in affected workflows.
The lesson is not that companies should stop using agents.
The lesson is that an agentic workflow is a product with a threat model.
In the War of the Ecosystems framework, this matters because every major platform wants its agents to sit closer to the work. The more an ecosystem connects models to repositories, tickets, customer relationship management records, data platforms, email, documents, cloud tools, and automation engines, the more it becomes a command surface.
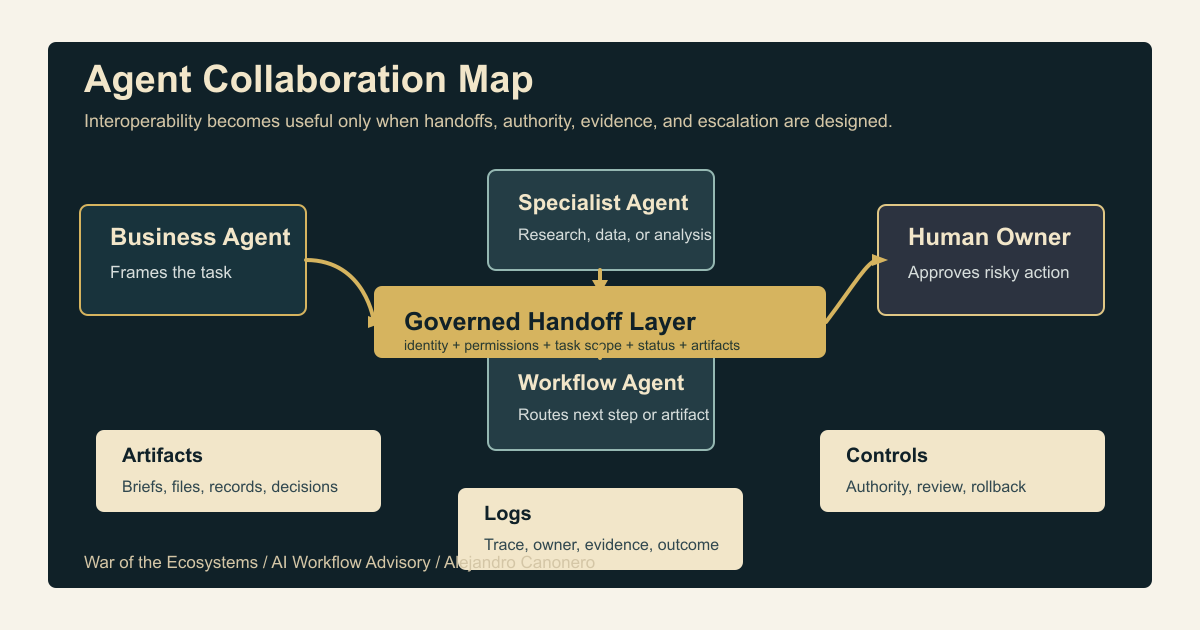
That command surface creates value only if the organization can govern what gets in, what the agent can see, what the agent can do, and how the result is verified.
When agents can act, the command surface is also the security surface.
1. The Attack Surface Is The Workflow
Traditional application security often starts with obvious boundaries: user login, database access, application programming interface permissions, input validation, network exposure, and deployment controls.
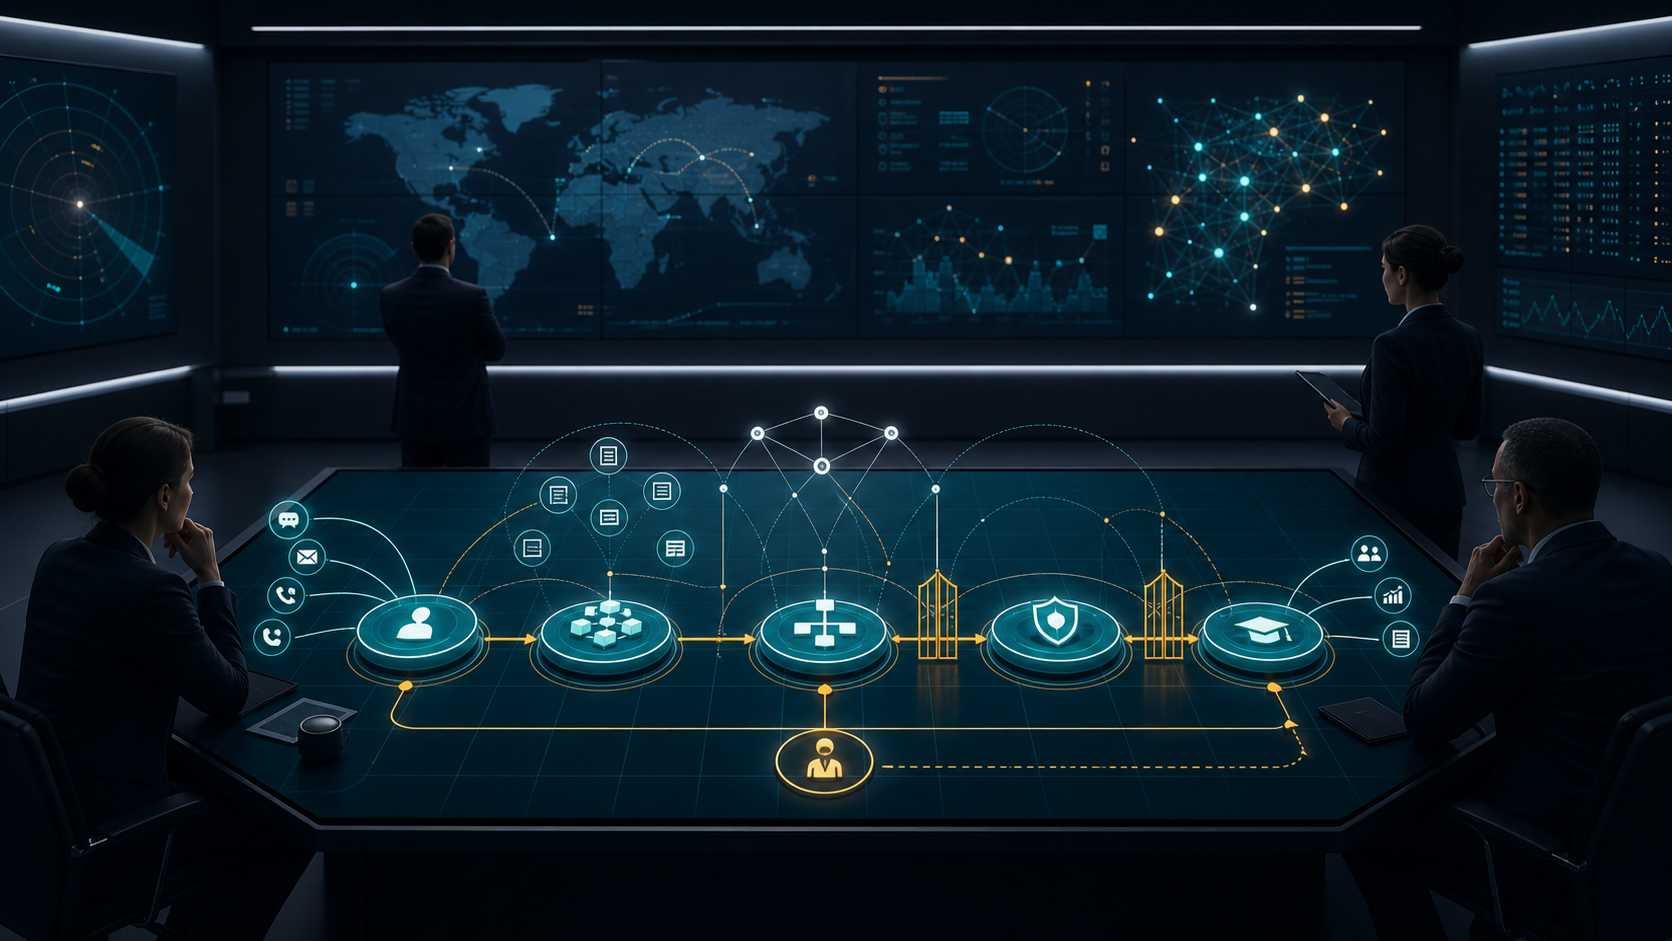
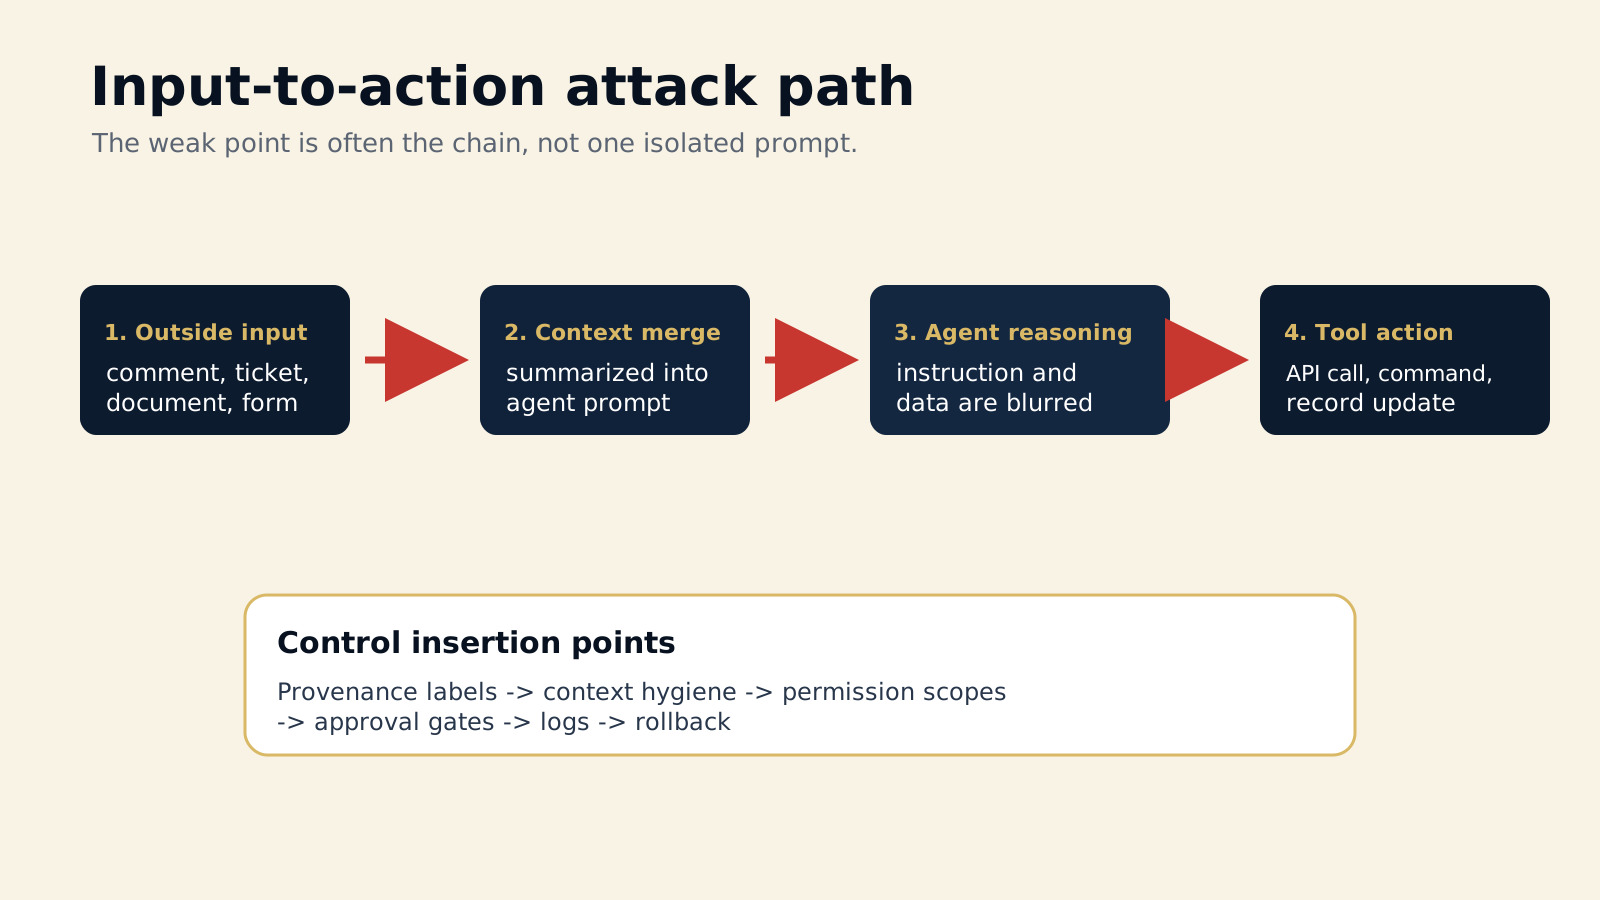
Agentic workflows add a different layer. The system may collect text from issues, comments, chat messages, documents, emails, forms, or task descriptions. That text may be summarized, embedded, retrieved, reformatted, merged into a prompt, passed through a tool, and then used by an agent that can call systems.
The dangerous part is the chain.
An untrusted input does not have to look like code. It can be ordinary language. It can hide inside a context object. It can travel through automation logic. It can become persuasive because the model receives it alongside legitimate task instructions.
If the workflow then gives the agent too much authority, the input can push the system toward an action the business never intended.
OWASP's large language model security work captures the broader pattern: prompt injection can manipulate model behavior through crafted inputs, and insecure output handling can turn model output into downstream system risk. In agentic workflows, those risks become more concrete because the model is not only writing text. It may be deciding what tool to call next.
That is the executive shift.
The question is not only whether the model can answer correctly. The question is whether hostile or untrusted context can make the workflow do something it should not do.
2. The War Of The Ecosystems Reading
This is not a narrow security footnote. It is a platform-power issue.
Every major ecosystem wants to become the place where artificial intelligence agents receive context, coordinate work, call tools, and produce outcomes. That may be a cloud platform, productivity suite, software-development platform, customer platform, data platform, enterprise resource planning system, or automation hub.
The vendor that owns this layer can shape the rules of work. It can decide what context is easy to include, which tools are conveniently available, which approvals are native, which logs are visible, and which integrations become default.
That is ecosystem command.
But platform envelopment has a security side. When one ecosystem surrounds the workflow, it also concentrates trust. A badly scoped connector, overprivileged agent, weak provenance model, or missing approval gate can turn convenience into exposure.
The strategic decision for clients is therefore not just which agent platform is strongest. It is where command should live, which actions must remain under internal control, and which guardrails are non-negotiable before the workflow scales.
3. Battlefield Example: Operation Greif
Operation Greif during the Battle of the Bulge is a useful military example because it was about trust, identity, and the flow of commands under pressure.
“Operation Greif during the Battle of the Bulge is a useful military example because it was about trust, identity, and the flow of commands under pressure.”
, Dr. Alejandro Canonero, DBA, author of War of the Ecosystems
German commandos used captured Allied uniforms and equipment to move behind American lines. The National WWII Museum describes the operation as an attempt to use espionage and sabotage to sow confusion in the Allied rear, including cases where disguised teams misdirected traffic and disrupted communication.
The operation did not achieve its original strategic objective, but it created exactly the kind of local confusion that exposed the importance of identity checks, trusted routes, and command verification.
That is the analogy for agentic workflows.
The attacker does not need to defeat every system head-on. It may be enough to enter the workflow through a trusted-looking channel, distort the agent's context, and trigger a downstream action before the organization realizes that the instruction came from the wrong source.
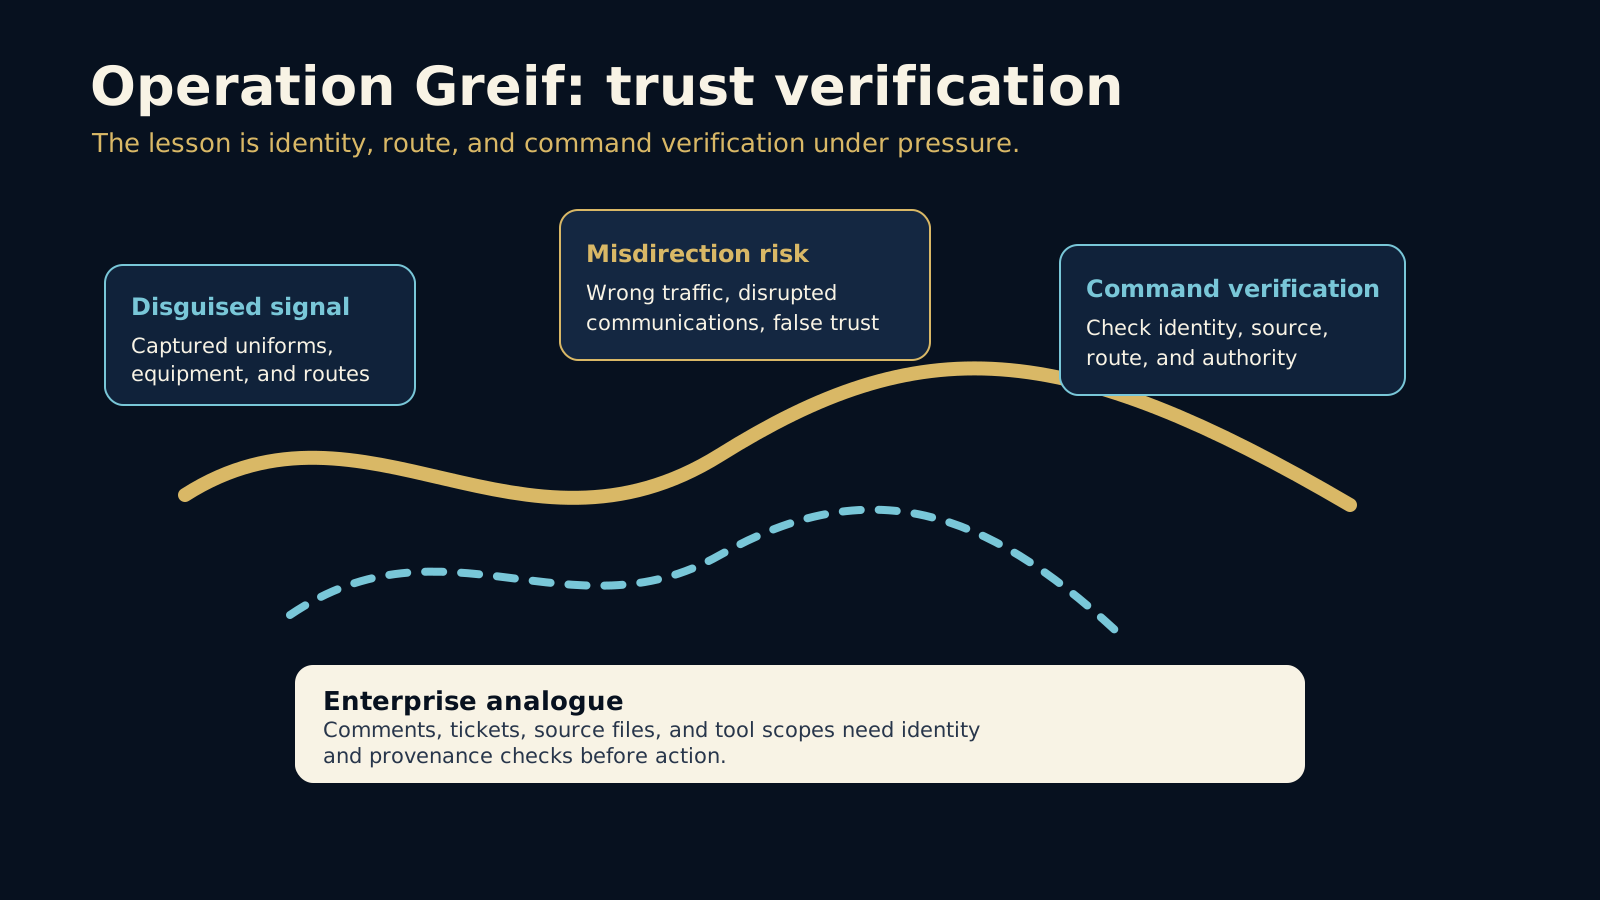
In the military setting, uniforms, signs, roads, orders, and radio links were part of the operating context. If that context was polluted, the unit could move in the wrong direction or trust the wrong signal.
In the enterprise setting, comments, tickets, records, prompts, source files, approvals, connectors, and tool scopes are part of the operating context. If that context is polluted, the agent can draft the wrong response, expose sensitive content, trigger a command, update a record, notify the wrong group, or escalate a false incident.
The lesson is not paranoia. The lesson is verification.
4. Controls Are Part Of The Product
Many companies will make the mistake of treating controls as a post-launch security checklist.
That is backwards.
The control model is part of the artificial intelligence workflow product. It decides what the workflow is allowed to become.
A useful agentic workflow needs at least six control layers.
This is not bureaucracy. It is command design.

5. The Client Diagnostic
A practical client should not begin by asking whether all agentic artificial intelligence is safe.
That question is too abstract.
Start with one workflow and map the control path.
Input surfaces
Name every outside source that can enter the workflow: comments, tickets, source files, records, emails, documents, forms, and chat messages.
Agent authority
Separate read-only work from draft, recommendation, approval-gated, and executable actions.
Evidence and rollback
Confirm what is logged, who owns the incident, how the workflow pauses, and how a wrong action is reversed.
For a software team, the workflow might be issue triage, code review, dependency updates, test repair, or deployment support. For a commercial team, it might be lead enrichment, proposal drafting, account-risk monitoring, or customer relationship management update recommendations. For finance, it might be variance commentary, invoice exception handling, or close-status reporting.
The same principle applies in each case.
If the agent can act, then the input path, permission path, evidence path, and recovery path must be designed.
6. The Strategic Lesson
The War of the Ecosystems is moving from model competition to workflow command.
That makes agentic security a strategic topic, not a technical footnote.
The winning ecosystem will not only make agents easier to create. It will make them safer to operate inside real work. It will help clients separate instruction from data, scope authority, preserve provenance, approve sensitive actions, monitor behavior, and recover quickly when something goes wrong.
That is also where independent advisory value appears.
Clients do not need fear-based artificial intelligence security theater. They need a sober map of where the workflow can be influenced, what authority the agent has, and what guardrails turn autonomy into controlled operating leverage.
Agentic workflows can be attacked.
So controls are not a drag on innovation.
Controls are how the workflow becomes trustworthy enough to matter.
The Decision
Do not scale an agentic workflow until you know where untrusted input enters, how context is transformed, what tools the agent can call, which actions require approval, what evidence is preserved, and who can stop or reverse the workflow.
The right executive question is not whether the agent sounds intelligent. The right question is whether the workflow is commanded.
Source Evidence
- Comment and Control: Hijacking Agentic Workflows via Context-Grounded Evolution, arXiv
- Comment and Control HTML version, arXiv
- Top 10 for Large Language Model Applications, OWASP
- AI Risk Management Framework and Generative AI Profile, NIST
- Operation Greif: The Secret Mission To Sow Chaos In The US Army, The National WWII Museum
Independent synthesis by Dr. Alejandro Canonero, DBA. Historical examples are used as strategic analogies. Source organizations do not endorse this interpretation.